Compare service operations, browser-state requirements and observation fidelity on one authorized task instead of treating stealth claims as a selection score.
Choose Camofox, a direct browser library or an HTTP fetcher by evidence needsCamofox BrowserREST
Follow a minimal localhost REST workflow with explicit identity, authentication and snapshot checks before attempting actions or importing credentials.
Camofox quickstart: create a test tab, read a snapshot and verify the resultCamofox BrowserREST
Create a replayable owned-page test suite that links observations to actions and catches semantic extraction errors without relying on public-site experiments.
Build a Camofox observation lab: stale refs, long pages and typed extractionCamofox BrowserREST
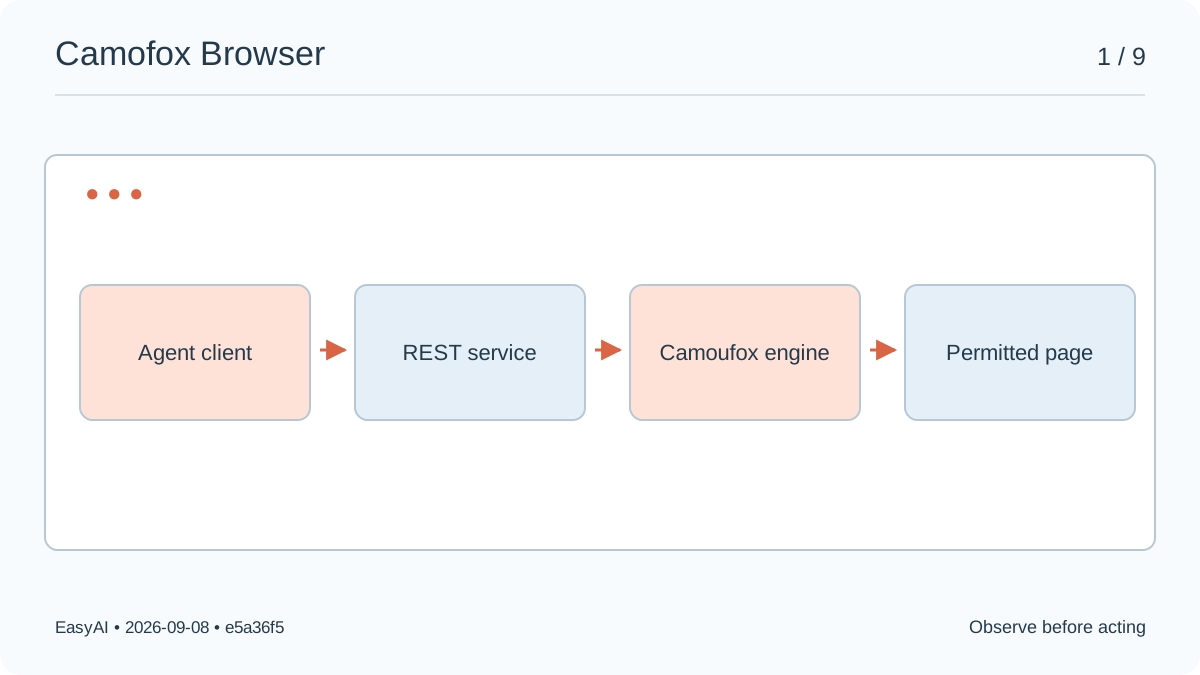
Separate Camofox’s REST service from the Camoufox engine, understand accessibility snapshots and element references, and define an authorized first use.
Camofox Browser explained: a browser service for agents, not just an HTML scraperCamofox BrowserREST