← Back to open sourceFeatured starting point
Trace the sandbox, trusted supervisor and gateway before adopting the project’s security claims
OpenShell explained: where an AI agent is allowed to actOpenShellnvidia/openshell
Start reading →Suggested learning path
01 → 09
01·3 min read·Search intent: Learning
Trace the sandbox, trusted supervisor and gateway before adopting the project’s security claims
OpenShell explained: where an AI agent is allowed to actOpenShellnvidia/openshell
·3 min read·Search intent: Learning
Create a disposable local sandbox without mistaking CLI installation for agent setup
OpenShell quickstart: inspect the installer and first sandboxOpenShellnvidia/openshell
·3 min read·Search intent: Learning
Plan a deployment around the trusted supervisor and the workload’s only network path
Deploying OpenShell: runtime fences, gateway and release matchingOpenShellnvidia/openshell
·3 min read·Search intent: Learning
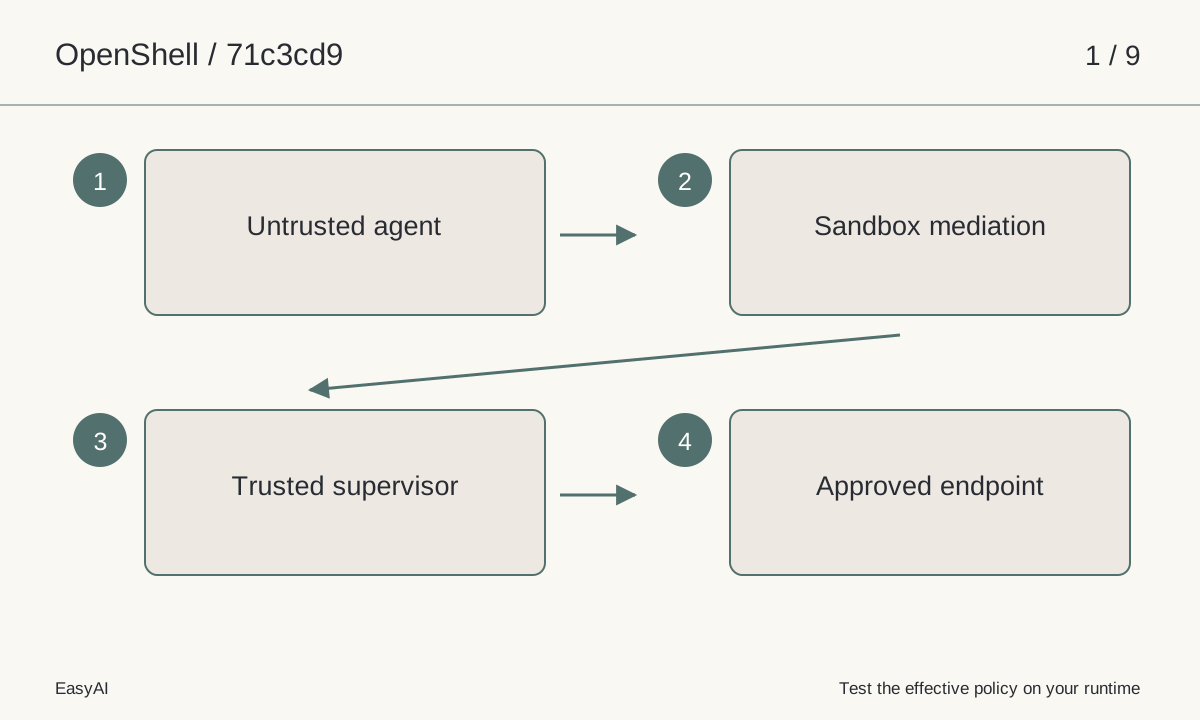
Follow a DNS or TCP request from the agent to an approved external endpoint
OpenShell architecture: a request crosses two trust boundariesOpenShellnvidia/openshell
·3 min read·Search intent: Learning
Use three small source entry points instead of treating the whole Rust workspace as one security module
Reading OpenShell source: policy updates, prover and mediationOpenShellnvidia/openshell
·3 min read·Search intent: Learning
Build a benchmark that separates startup, mediation and provider charges
OpenShell performance and cost: measure the boundary you useOpenShellnvidia/openshell
·3 min read·Search intent: Learning
Verify the selected policy and the runtime fence before trusting an agent workload
OpenShell security operations: policy provenance and credential pathsOpenShellnvidia/openshell
·3 min read·Search intent: Learning
Compare the actual control boundary with simpler and heavier alternatives
Choosing OpenShell for agent isolationOpenShellnvidia/openshell
·3 min read·Search intent: Learning
Turn the documented controls into a small reviewable operational report
An OpenShell adoption pilot with evidence and rollbackOpenShellnvidia/openshell